Security+ SY0-801 Complete · the whole examPass Security+ knowing you’re ready for every domain.
One guide for the whole SY0-801 exam: every domain of the outline, the 490 practice questions that prove you know it, and nothing left to buy later.
This guide comes with the Complete Security+ Collection
Guides are sold one certification at a time. Bought single domains before? Sign in first and what you paid comes off at checkout.
Studying for more than one exam?
- Interactive online guide
- Downloadable PDF
- Lifetime updates
- 30-day money-back guarantee
Secure checkout via Stripe · no account needed · instant access
Studying hard isn't the same as knowing you're ready.
Too much to cover
Security+ spans 5 domains, and the books, videos and open tabs keep piling up. You’re studying hard, but you can’t tell if it’s the right material.
No way to know you’re ready
So you book the exam, feel your stomach drop, and push the date back. The doubt costs more study time than the material does.
Expensive to guess wrong
A Security+ voucher is $439 and doesn’t include a retake. You shouldn’t have to pay CompTIA to find out what you didn’t know.
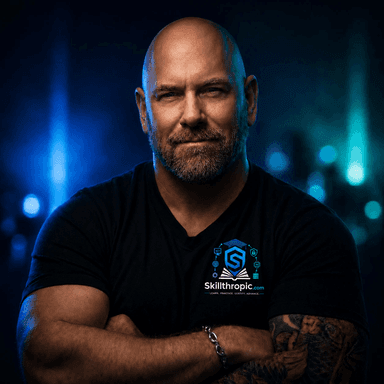
I've taught this to 700,000 people. Let me help you pass Security+.
I’m Chris Rees. I’ve spent 25 years in IT and built 55 courses on Pluralsight. The question I hear most isn’t about the material. It’s “am I ready?”
This guide is my answer for Security+: the whole published outline, in plain English, then exam-style questions that explain why the right answer is right and why the tempting one is wrong.
- students taught *
- 700,000+
- students taught *
- from 2,007 ratings
- 4.6/5
- from 2,007 ratings
- Pluralsight courses
- 55
- Pluralsight courses
- years in IT
- 25+
- years in IT
* From Chris's Pluralsight author dashboard. Course count and ratings are public on his profile.
More about ChrisThree steps from “am I ready?” to passed.
Step 1
Find your gaps
Take the free readiness quiz. It scores you domain by domain, so you know where to start. No email needed.
Step 2
Study what’s on the test
Work through all 28 modules in exam order, with 490 practice questions along the way.
Step 3
Book it with confidence
When you’re scoring well in every domain, book the exam knowing you’ve covered everything CompTIA can ask.
Your whole exam, in one guide
Every domain and every subdomain of the SY0-801 outline, in the order and proportion the exam weights them. One purchase, nothing left to buy later.
Every objective, nothing extra
Built line by line from the official CompTIA Security+ objectives 1.1–5.6: 217 in-depth topics with worked scenarios and exam tips, in a 696-page guide you'll actually finish.
490 exam-style questions
Every question comes with instant feedback and a full explanation, so a wrong answer teaches you as much as a right one.
The industry's baseline cert
Security+ is the most widely held cybersecurity certification in the world: the default HR filter for security roles and the baseline for DoD 8140 work.
Serving, transitioning, or a military spouse?
Security+ appears in the DoD 8140 qualification matrix. See how it maps to work roles, which credentialing program your branch runs, and what it will and will not pay for. Read the DoD 8140 guide →
Read a real excerpt, free
This is the actual opening of Module 1.1, Security concepts & controls, not marketing copy. If you like how it teaches, the rest of the guide reads the same way.
Explain security concepts and controls.
The vocabulary the rest of the exam assumes: defense in depth and the principles that sit under it (CIA, AAA, non-repudiation, Zero Trust, least privilege), then the two ways every security control is classified: by category (how it is implemented) and by type (what it is meant to do).
At 02:10 on a Tuesday, Microsoft Sentinel pages Jordan Avery, security administrator at Ridgeline Health Partners. A night-shift nurse at the Olympia clinic opened an invoice attachment that slipped past the email filter. The macro ran, and Defender for Endpoint saw Word spawn PowerShell, killed the process and isolated the workstation. The nurse’s account had no local administrator rights, the clinic VLAN cannot reach the ChartWell database servers directly, and the one credential the malware did capture was useless without a second factor. By 02:40 Marcus Bell, the SOC lead, closes the incident as contained: one workstation to reimage, no patient data touched.
Nothing about that night was luck. Two controls failed (awareness training and the email filter), and the ones behind them did not. That is the whole of objective 1.1 in one incident: layers of controls, each built on a small set of principles, each classifiable by how it is implemented and what it is supposed to accomplish. The next morning Priya Nair, the CISO, asks Jordan to “map what worked to our control framework,” which is exactly the skill this objective tests.
Defense in depth
Defense in depth is the practice of placing multiple, overlapping controls between an attacker and an asset so that the failure of any single control does not result in compromise. Every control has a failure rate. Filters miss messages, people click, patches arrive late. If the layers fail independently, an attacker has to beat all of them in sequence, and each one that holds also buys time for detection and response.
SY0-701 did not list defense in depth as an objective bullet. SY0-801 makes it the heading that CIA, AAA, non-repudiation, Zero Trust principles and least privilege sit under, and it pulls least privilege forward from the mitigation and access control objectives. Two wording changes: the control type is now written “Deterring” (701 said “Deterrent”), and the categories carry paired names (Technical/logical, Managerial/administrative, Physical/environmental). Zero Trust is cut down to principles here; the control plane and data plane architecture is taught in 3.2.
Try 3 sample questions
Pulled straight from the guide’s 490-question bank. Tap an answer for instant feedback and the explanation.
From module 1.1 · Security concepts & controls
1. During a firmware audit, a biomedical engineer finds that the drug library on several infusion pumps was modified so that the maximum dose limit for one medication is ten times higher than the approved value. No data left the network and the pumps stayed online. Which security property was PRIMARILY violated?
From module 1.2 · Change management & security
1. A network engineer argues that firewall changes do not need to go to the change advisory board (CAB) because the network team already understands every rule. Which statement BEST explains why the CAB, with security as a member, reviews the change anyway?
From module 1.3 · Cryptographic solutions
1. Dr. Alan Reyes wants to send a file to Grace Lindqvist so that only Grace can read it, using asymmetric encryption. Which key must be used to encrypt the file?
487 more questions like these are waiting inside.
What's inside
The whole CompTIA Security+ SY0-801 exam in one technical guide: all five domains and all 27 objectives, taught line by line from the official exam objectives. Real commands, logs, configurations and worked calculations instead of definitions, one healthcare network followed from change control to incident response, everything new in SY0-801 flagged where it appears, and a question bank that explains why every wrong answer is wrong.
- 27 modules, one per objective, covering all 5 domains (1.1–5.6)
- 400 practice questions, nearly half of them detailed scenarios with logs, configs and calculations
- A 90-question practice exam with a 90-minute timer, flag-and-return, and a score by domain and objective
- Explanations that say why the right answer is right and why each wrong option is wrong
- 57 worked scenario workshops, 67 charts and diagrams, and 172 reference tables
- Everything new in SY0-801 flagged, including the AI threats objective (2.6)
- 696-page downloadable PDF for offline study and printing
- Lifetime updates as the exam evolves
The modules, mapped to the objectives
- 1.120 Qs
Security concepts & controls
Explain security concepts and controls.
Defense in depthCIA triadAAA (authentication, authorization, accounting)Non-repudiationZero Trust principlesLeast privilegeControl categoriesCompensating control - 1.220 Qs
Change management & security
Given a scenario, demonstrate the impact of change management processes on security.
Change advisory board (CAB)Impact analysisBackout planningFail forwardMaintenance windowAllow lists/deny listsDependenciesVersion control - 1.324 Qs
Cryptographic solutions
Explain the importance of using appropriate cryptographic solutions.
Public key, private key & key escrowCertificate authority & root of trustCSR, wildcard, CRL & OCSP staplingSymmetric, asymmetric & hybrid encryptionEncryption levels: full disk to recordKey exchange & forward secrecy (ECDHE)Digital signatures, hashing & saltingTPM, HSM, KMS & obfuscation - 2.114 Qs
Threats & vulnerabilities
Explain characteristics of threats and vulnerabilities.
Threat feedSTIX and TAXIILikelihood and impactThreat intelligence life cycleTraffic Light Protocol (TLP)CVSS base, temporal/threat and environmental metricsKEV and EPSSCVE, CWE and NVD - 2.212 Qs
Threat actors & motivations
Describe common threat actors and motivations.
Crime syndicate/organized crimeState-sponsored actorInsider vs. accidental/unintentionalHacktivist vs. terroristCompetitor & intellectual propertyExtortion vs. financial motivationInternal/externalResources/funding & sophistication/capability - 2.318 Qs
Threat vectors & sources
Describe threat vectors and sources.
Advanced persistent threat (APT)DMARC alignment and spoofed sendersQR phishing and fake CAPTCHA (ClickFix)Session token theft and AiTM phishingSession keys and forward secrecyLiving-off-the-land and built-in toolsSupply chain: MSP, logistic and SaaS providersUSB keyboard emulation (HID attack) - 2.418 Qs
Vulnerabilities & attack surfaces
Explain types of vulnerabilities and attack surfaces.
Unsupported vs unpatched vs unmanagedTime-of-check / time-of-use (TOC/TOU)Malicious updateHardcoded secretsUnsafe exception handlingZero-dayUnmanaged/stale credentialsPublic object storage - 2.522 Qs
Indicators of malicious activity
Given a scenario, analyze indicators of malicious activity.
Fileless malwareReflection and amplificationOn-path attackDNS cache poisoningIndicator of compromise (IoC)Impossible travelPassword sprayingMFA bypass - 2.612 Qs
AI threats & vulnerabilities
Summarize threats and vulnerabilities associated with artificial intelligence (AI) usage.
Poisoning vs. model manipulation vs. evasionDirect and indirect prompt injectionJailbreaking and guardrailsHallucinations and slopsquattingBias and the four-fifths ruleExplainability (black box)Shadow AI and permission-aware retrievalExcessive agency and code execution - 3.118 Qs
Architecture models & security
Compare and contrast security implications of different architecture models.
Deployment models (public, private, community, hybrid)Shared responsibility modelInfrastructure as Code (IaC)Operational technology (OT)Air-gapped networkLogical vs. physical segmentationData sovereigntyServerless execution role - 3.220 Qs
Managing the security architecture
Given a scenario, manage the security architecture to best protect the infrastructure.
Security zones and device placementAttack surfaceZero Trust architectureApplication access control (ZTNA)Out-of-band managementSecurity Service Edge (SSE)Group Managed Service Account (gMSA)Fail-open vs. fail-closed - 3.320 Qs
Data protection concepts & strategies
Summarize concepts and strategies used to protect data.
Structured vs. unstructured dataData at rest, in transit, in useTokenization vs. encryptionData transpose (shuffling)Deidentification and pseudonymizationData owner vs. data custodianMarking and labelingRetention, legal hold and disposal - 3.418 Qs
Resilience & recovery
Explain the importance of resilience and recovery in security architecture.
Hot, warm and cold sitesPlatform diversityHigh availabilityQuorum and split brainImmutable backupRestoration testingFailover testRTO and RPO - 4.120 Qs
Mitigating controls & solutions
Given a scenario, apply mitigating controls, techniques, and solutions to secure the environment.
SegmentationCanary accountAllow list vs. block listInline IPS vs. passive IDSRate limiting802.1X and endpoint postureSecrets scanningDMARC alignment - 4.28 Qs
Asset management life cycle
Explain the security implications of proper hardware, software, and data asset management.
Asset management life cyclePlanning/scopingOwnership and classificationInventory and enumerationSanitization: clear, purge, destroyCryptographic eraseCertificate of destructionData retention and legal hold - 4.312 Qs
Vulnerability management tasks
Given a scenario, perform tasks associated with vulnerability management.
Credentialed vs. non-credentialed scanFalse positive and false negativeInternet Protocol Address Management (IPAM)Cloud security posture management (CSPM)CVSS, CVE, CWE and CISA KEVCompensating control and exceptionRescan and retest (verification)Bounty program vs. responsible disclosure policy - 4.414 Qs
Alerting & monitoring
Explain security alerting and monitoring concepts and tools.
Log aggregationAlert tuningFalse positive / false negativeSIEM correlationOrchestration (SOAR)NetFlow / SNMP / syslog / SCAPPort mirroring (SPAN)Network management system - 4.518 Qs
Identity & access management
Given a scenario, apply concepts related to identity and access management.
Joiner, mover, leaver life cycleFederation (IdP and SP)SAML assertion vs OAuth access tokenEmergency access (break-glass) accountPhishing-resistant MFA and passkeysMandatory vs discretionary access controlJust-in-time privileged accessAccess review (recertification) - 4.612 Qs
Automation, orchestration & AI
Given a scenario, apply automation and orchestration solutions to secure operations.
Orchestration and SOARDesired state managementConfiguration drift and idempotenceGuardrailsAutomation logicAgentic AIAI-augmented baselinesCI/CD pipeline security gates - 4.712 Qs
Incident response activities
Summarize concepts associated with incident response activities.
Tabletop exercise vs. simulationPlaybook and incident response rolesInternal and external advisoryThreat huntingOrder of volatilityChain of custody and legal holdQuarantine/isolationRoot cause analysis and post-incident reporting (PIR) - 4.812 Qs
Investigation data & sources
Given a scenario, use data, artifacts and sources to support a security investigation.
Access and accounting logs (logical and physical)Authentication vs. audit logsNetFlow/IPFIX vs. packet captureFile/log integrity (hashing, forwarding, event 1102)Order of volatility and memory dumpBit-level copy vs. snapshotStakeholders: HR, Accounts, LegalLog parsing (grep, regex, sort, uniq -c, KQL) - 5.19 Qs
GRC artifacts: policies to runbooks
Explain the importance of governance, risk, and compliance artifacts.
Policy, standard, procedure, guidelineBenchmark versus baselineAdvisoryReference architectureRequest for comments (RFC)SOP, runbook and playbookBusiness continuity and disaster recovery plansVulnerability disclosure policy (VDP) - 5.211 Qs
Risk management processes
Explain the impact of risk management processes on the security of the organization.
Risk registerCurrent mitigationsResidual riskRisk appetiteRisk treatment (transfer, accept, avoid, mitigate)Business impact analysis (BIA)SLE, ARO and ALEQualitative vs. quantitative analysis - 5.310 Qs
Third-party risk management
Explain the assessment and management processes associated with third-party risk.
Request for proposal (RFP)Due diligenceMaster services agreement (MSA)Service-level objective (SLO)Right to auditVendor registryVendor lock-inRules of engagement - 5.48 Qs
Effective security compliance
Summarize elements of effective security compliance.
AttestationAcknowledgementAML/CTFRight to be forgottenProcessing restrictionController vs. processorLegal holdData retention schedule - 5.510 Qs
Audits, assessments & pen testing
Explain concepts associated with audit and assessment activities.
Sampling, deviation rate & sampling riskAssertion vs. attestationMITRE ATT&CK, Cyber Kill Chain, Diamond ModelAudit charter & audit committeeGap analysis vs. benchmarkingSOC 2 Type 1 vs. Type 2Known, unknown & partially known environmentFunctional vs. behavioral testing - 5.68 Qs
Security awareness in practice
Given a scenario, apply security awareness concepts to improve organizational security.
Targeted trainingCorrective trainingLearning management system (LMS)Report rateManagerial reportsPersonnel behavior risk scoringBusiness email compromise (BEC)Operational security (OPSEC) - PE90 Qs
Full-length practice exam
90 mixed-domain questions weighted like the real SY0-801 exam
Time management: 90 questions, 90 minutesFlag and returnFIRST / BEST / MOST qualifiersReading exhibitsReview by objective numberReadiness threshold
All 5 domains comes in the Complete Security+ Collection.
Every domain of the exam, this one included, for $69, one time.
See everything insideSame exam. Two very different months.
Studying without a plan
- Re-reading the same chapter because you’re not sure what matters
- Booking the exam, then pushing it back. Twice.
- Walking out unsure, and paying $439 to sit it again
Studying with Skillthropic
- Every domain of the SY0-801 outline, in the order the exam lists it
- 375 practice questions that show you exactly where you stand
- Booking the exam because you’re ready, not because the date arrived
Questions, answered
Do I need an account to buy?
No. Checkout is a single Stripe form: email and card, about 30 seconds. We create your access from your checkout email automatically and sign you in the moment payment completes.
Is this up to date with the real SY0-801 exam?
Yes. The guide is mapped module-by-module to the official CompTIA Security+ objectives (1.1–5.6), and lifetime updates are included, so as the exam evolves your guide does too.
What exactly do I get?
Instant access to this guide: the interactive online version with all 490 practice questions, plus a 696-page PDF you can download, print, and keep forever. It comes with the Complete Security+ Collection, so you also get the 5 domain guides in it.
Can I buy this guide on its own?
No. Study guides are sold one certification at a time, so this guide comes with the Complete Security+ Collection for $69, one-time. If you already own the Collection, this guide is already in your account at no extra cost.
What if it isn't for me?
Every purchase comes with a 30-day money-back guarantee. Email us and we'll refund you, no hoops.
Who wrote it?
Chris Rees, a professional information technologist with 25+ years in IT and the author of 55 certification courses published on Pluralsight, rated 4.6/5 across 2,007 ratings.
Be ready for the whole SY0-801 exam, for $69
Instant access, lifetime updates, and a 30-day money-back guarantee. The only risk is walking into the exam without it.
Get the Collection