Feeds, Confidence, and the Pyramid of Pain: Threat Intelligence and Threat Hunting the Way CySA+ Tests Them
Chris Rees
25+ years in IT · Pluralsight author, 4.6/5 across 2,000+ ratings
 www.skillthropic.com
The sector sharing group sends a report about a group targeting hospital scheduling systems. No hash, no address, no signature. It describes behavior: initial access through a vendor's remote access tool, credential harvesting from browser stores, staging data in a folder named like a backup job. A candidate who thinks intelligence means a blocklist sees nothing usable. Objective 1.4 exists to make sure you recognize the most valuable intelligence you will get all year, and know what to do with it.
Who you are defending against
The objective opens with threat actors, and it names two specifically because they break the assumptions the rest of the SOC runs on.
| Actor | Defining property | What it means for detection |
|---|---|---|
| Advanced persistent threat (APT) | persistence and intent, not necessarily sophistication; well resourced, often state sponsored, pursuing one objective for months | eviction is a setback, not an ending; expect a return through a different door |
| Insider: malicious | legitimate access used deliberately | activity is authorized, so only the pattern is abnormal |
| Insider: negligent | harm through carelessness; by far the most common insider | training and guardrails, not hunting |
| Insider: compromised | a legitimate user whose credentials someone else is operating | looks like the user until the behavior does not |
| Organized crime, hacktivists | money or ideology, opportunistic | fast, noisy, commodity tooling, low persistence |
The exam's angle is the word persistent. An APT is defined by the fact that it comes back, so intelligence about how it operates outlives any indicator you block. The insider split matters because the three kinds need three different controls: a warning before the click for the negligent, behavioral analytics for the compromised, both plus data monitoring for the malicious.
Where intelligence comes from
The objective groups sources by who can see them and what that costs.
- Open source (OSINT). Vendor research, security blogs, public malware repositories, code and DNS records, social media. Free, abundant, and uneven in quality and timeliness.
- Closed source and proprietary. Paid vendor feeds and membership-restricted research. More curated and more timely, usually under terms that forbid redistribution.
- ISACs. Sector-specific Information Sharing and Analysis Centers. Their power is relevance: an adversary campaigning against hospitals reaches your peers before you, and their indicators arrive with context.
- Government bulletins. CISA advisories and national CERT alerts: authoritative, vetted, often the first public notice that a vulnerability is being exploited, and slower than a feed by design.
- Dark web. Forums and marketplaces where credentials, access and data are sold. Useful for learning that you are already a target or already breached; risky to collect from directly, which is why most teams buy it through a vendor.
A stem about "a sector-specific community that shares indicators among members" is describing an ISAC. One about "publicly available, unvetted" sources is describing OSINT, and the follow-up is always how much to trust it.
How much of it to believe
The objective names three dimensions of confidence, and the exam tests each as a separate failure.
| Dimension | The question | The failure it prevents |
|---|---|---|
| Timeliness | Is this still true? | blocking an address that was command and control four months ago and is now a shared cloud host |
| Relevancy | Does this apply to us? | consuming industrial control indicators for a sector you do not operate in: accurate, useless, distracting |
| Accuracy | Was it right to begin with? | an unvetted feed that lists a major content delivery network as malicious; blocking it blocks half the internet |
The intelligence cycle
Intelligence is a process, and the exam expects you to place activities in the right phase of it.
Requirements come from the decisions the organization needs to make: which actors target our sector, which assets they want, which techniques our architecture is exposed to. Collection gathers from the sources above. Analysis applies the confidence dimensions and turns raw data into a judgment with a confidence level attached. Dissemination delivers it to whoever can act: an indicator list to the SOC, a hypothesis to the hunt team, a briefing to leadership. Feedback reports what was useful, which rewrites the requirements. A team drowning in indicators nobody asked for is a requirements failure, not a collection one; an accurate report that reached the SOC a week late is a dissemination failure.
Sharing it without retyping it
Intelligence that stays in a PDF is intelligence a machine cannot use. Three standards let it move.
- STIX is the language: a structured format for describing indicators, actors, campaigns, attack patterns and the relationships between them.
- TAXII is the transport: the protocol for exchanging STIX content, typically as a server that clients poll for a collection of intelligence they subscribe to.
- OpenIOC is an older XML format for describing host indicators, still met in tooling and on the exam as the alternative to STIX.
The exam question is a matching one: STIX describes, TAXII delivers.
Indicators, and the pyramid that ranks them
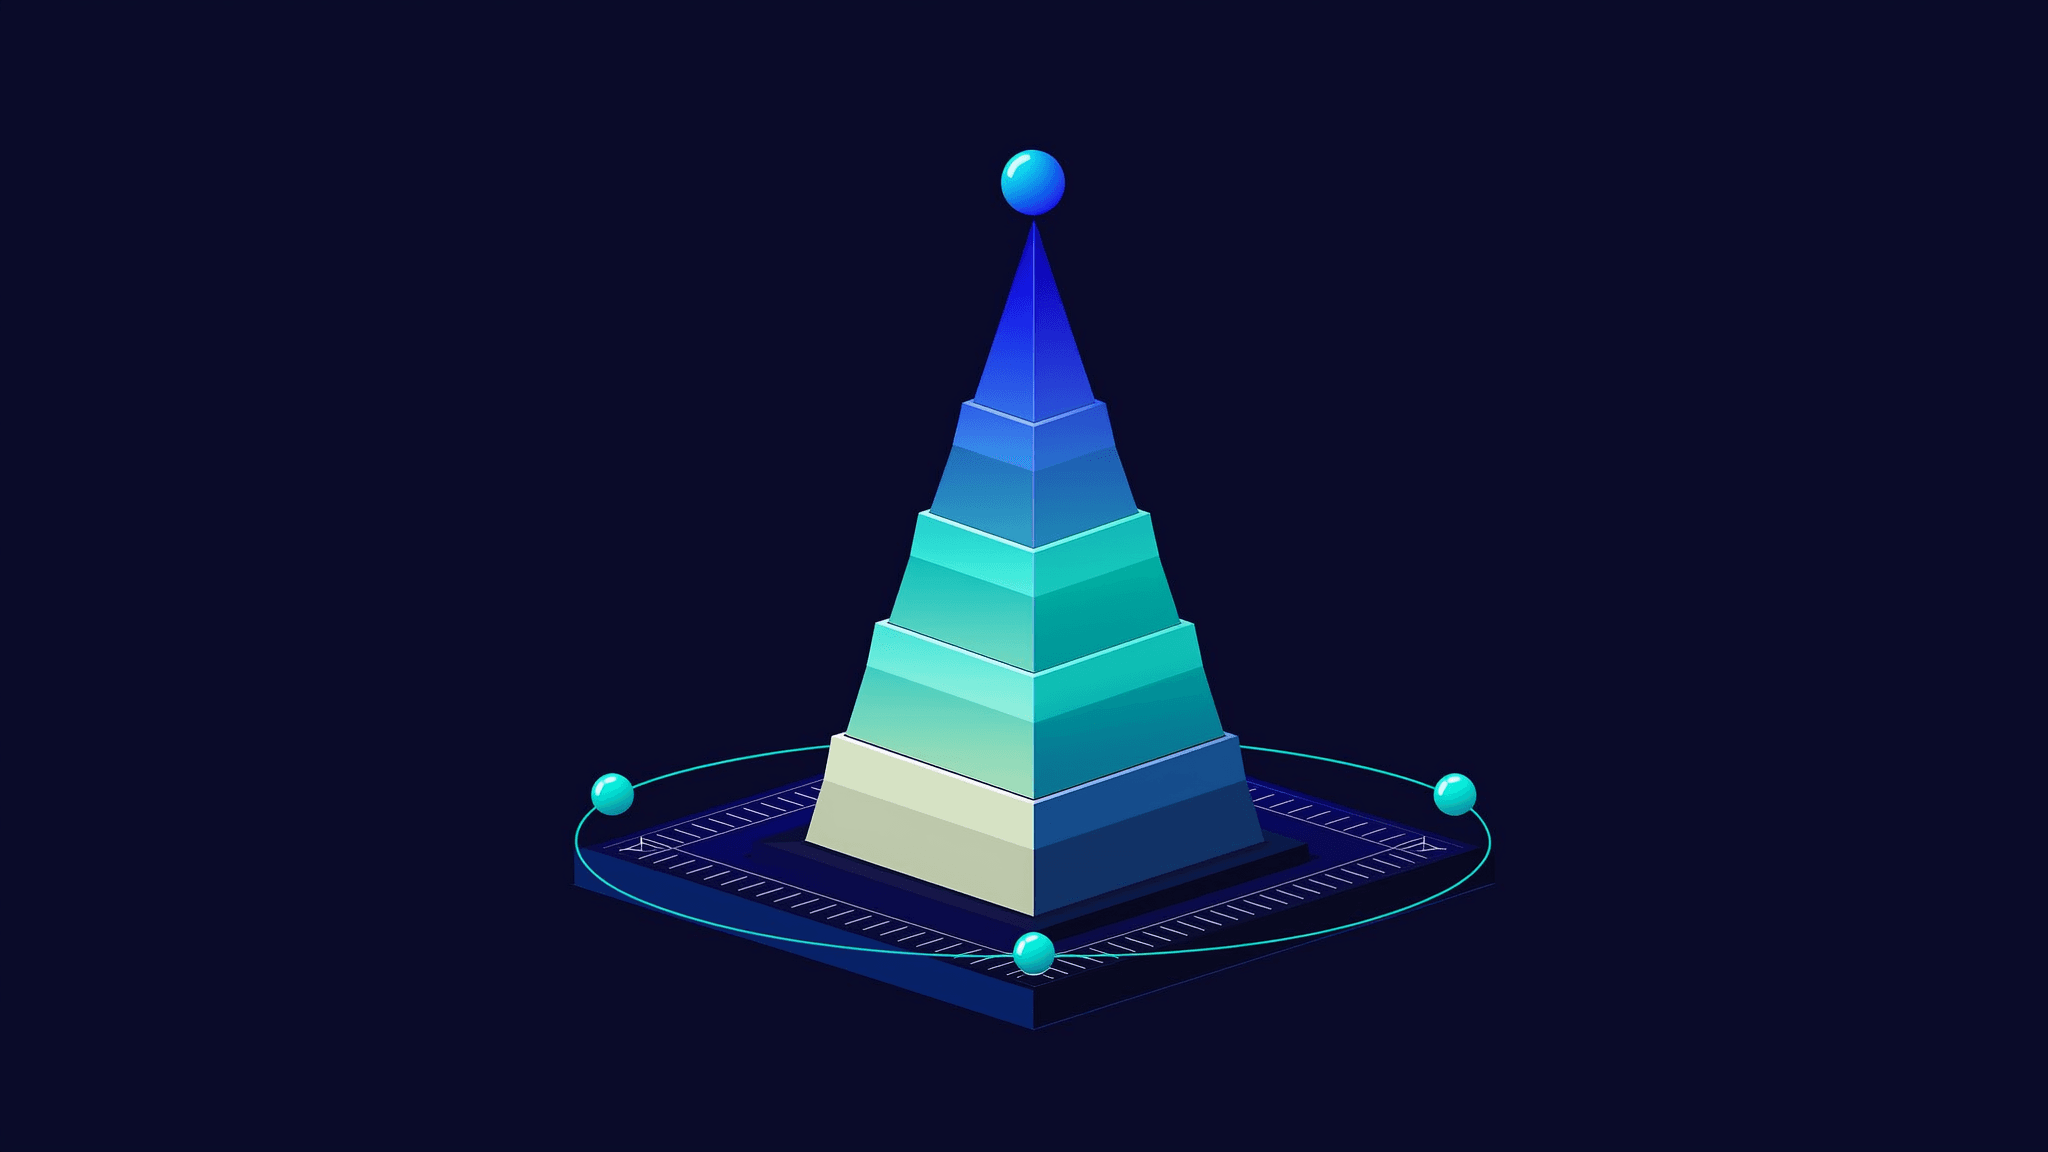
The objective splits indicators of compromise into a lifecycle (collection, analysis, application) and two types. An atomic indicator is an indivisible fact: a hash, an address, a domain. Easy to match, easy for the adversary to change. A behavioral indicator is a pattern of actions: a signed binary spawned by a document, then making an outbound connection, then writing to a startup location. Harder to write, far harder to evade. David Bianco's Pyramid of Pain ranks indicator types by how much it costs the adversary when you deny them, and the exam tests it by name.
The classic stem: defenders block a hash, the adversary returns within hours with recompiled binaries. What would have hurt more? The detail tells you which tier was blocked ("recompiled" means hashes, "new infrastructure" means addresses or domains) and the answer is always higher up. The catalog of the top tier is MITRE ATT&CK, which has its own post alongside the Kill Chain and Diamond Model. The ISAC report from the opening is a set of TTPs, which is why it was valuable without a single hash.
Hunting is not monitoring
Monitoring waits. A rule was written, traffic matched it, an alert appeared. Hunting starts from the opposite assumption: if an adversary were already inside, which of my rules would have failed to fire? Then it goes looking for what those rules would have missed. The exam distinguishes the two by their starting point: an alert starts monitoring, a hypothesis starts a hunt.
Hunts come in flavors the objective names. Hypothesis-driven hunting begins with a statement such as "an adversary is harvesting browser credentials," derived from intelligence, an ATT&CK coverage gap, or a known weakness, and asks what evidence would exist if it were true. IoC-driven hunting sweeps the estate for atomic indicators from a report: fast, and limited to the bottom of the pyramid. Hunting for indicators of attack looks for the behavior in progress, the sequence rather than the artifact, which is where TTP-based hunting lives and where durable detections come from.
The objective also names focus areas, because a hunt with no scope is a browse. Configurations and misconfigurations are where adversaries live longest: an exposed service, a permissive share, a forgotten account. Isolated networks, including operational technology and segments the SIEM does not reach, are hunted because nothing else is watching them. Business-critical assets are hunted first because that is where the adversary is going.
Active defense and honeypots invert the problem. Rather than separating malicious from benign in a flood of legitimate activity, you plant something no legitimate process has any reason to touch: a decoy system, a honeyfile named like a patient export, a honeytoken credential in a config file. Any interaction is high confidence by construction, because nothing good was ever supposed to be there.
Every hunt ends in one of two results, and both count. Either you find the activity, which becomes an incident, or you find nothing, which converts an unknown into a known. Either way the final step is to turn the hunt into a standing detection. That step is the one teams skip and the one that compounds; it is how a program climbs the pyramid, one hypothesis at a time.
Four stems, decoded
- A SOC blocks the hashes from a malware report; a week later the same group is back with recompiled binaries. Hashes were the tier blocked. Move up the pyramid: detect the technique, not the file.
- A pipeline ingests a community feed straight into the firewall blocklist, and users lose access to a major cloud service. Accuracy and timeliness were never evaluated. Vet, then monitor, then enforce.
- A hospital wants indicators specific to attacks on hospitals, with context from peers. An ISAC: closed, sector-specific, reciprocal, relevant by construction.
- With no alert to prompt it, an analyst asks whether browser credential stores are being read by anything other than a browser, and writes a query to find out. Hypothesis-driven threat hunting. Finding nothing is still a result, and the query becomes a detection.
Key takeaways
- APT means persistent, and insiders come in three kinds. Malicious, negligent and compromised need different controls; negligent is the most common.
- Sources trade cost for curation. OSINT is free and unvetted; closed feeds and ISACs are curated and relevant; government bulletins are authoritative; the dark web tells you that you are already a target.
- Timeliness, relevancy, accuracy. Each is a separate failure. Vet before you block.
- STIX describes, TAXII delivers, the cycle starts with requirements. Collection without a question produces intelligence nobody can use.
- The pyramid answers "what would have hurt more." Hashes are trivial, TTPs are tough; a hunt is a hypothesis, not an alert, and it ends as a detection.
Threat intelligence and threat hunting are objective 1.4 of CySA+ Domain 1, Security Operations, 34% of the exam, and they supply the hypotheses that SOC triage turns into work. Work all 36 topics with our free CySA+ Domain 1 study guide.
#CySAplus #CS0004 #ThreatIntelligence #ThreatHunting #PyramidOfPain #STIX #TAXII #BlueTeam #InfoSec #CyberSecurity
Keep reading
The Analyst's Toolkit: Which Tool Answers Which Question, From Wireshark to YARA
CySA+ objective 1.3 lists eighteen tools and the exam never asks what any of them is. It asks which one you reach for. The toolkit sorted by the question each tool answers: packet capture versus flow analysis, Snort and Suricata rule anatomy, SIEM correlation, EDR against the wire, the file analysis chain from Strings to YARA, and the workflow that turns a suspicious attachment into a hunt.
Read CySA+ deep divesCVSS, EPSS and KEV: Cutting 61,000 Findings Down to This Week's Work
Severity is not priority. What CVSS actually measures and the two metric groups almost nobody applies, how EPSS turns severity into probability, why the CISA KEV catalog ends most arguments, and a prioritization funnel that survives contact with a real vulnerability queue. CySA+ CS0-004 Domain 2.
Read CySA+ deep divesSOC Triage: Turning 40,000 Alerts Into the Handful That Matter
Security Operations is 34% of CySA+ CS0-004, and almost all of it is triage. How telemetry becomes an alert, what the true/false positive quadrant costs you, why the Pyramid of Pain decides which indicators are worth detecting, when to hunt instead of wait, and where AI helps in a SOC without being trusted.
ReadEnjoyed this? Get the AI security news that matters.
Join The AI Security Brief for the top AI security news, plus what's important to the C-suite. Free, straight to your inbox.
No spam. Unsubscribe anytime.
This is a third of your exam
Security Operations is the largest domain on CySA+ CS0-004 by some distance. Master all 36 topics across six objectives, including 1.6, AI in security operations, with a running SOC scenario and 120 practice questions.
Get the CySA+ Domain 1 guide